Blog

Computer System Validation Process: 7 Key Steps for GMP Compliance
October 23, 2026 Incepbio Marketing
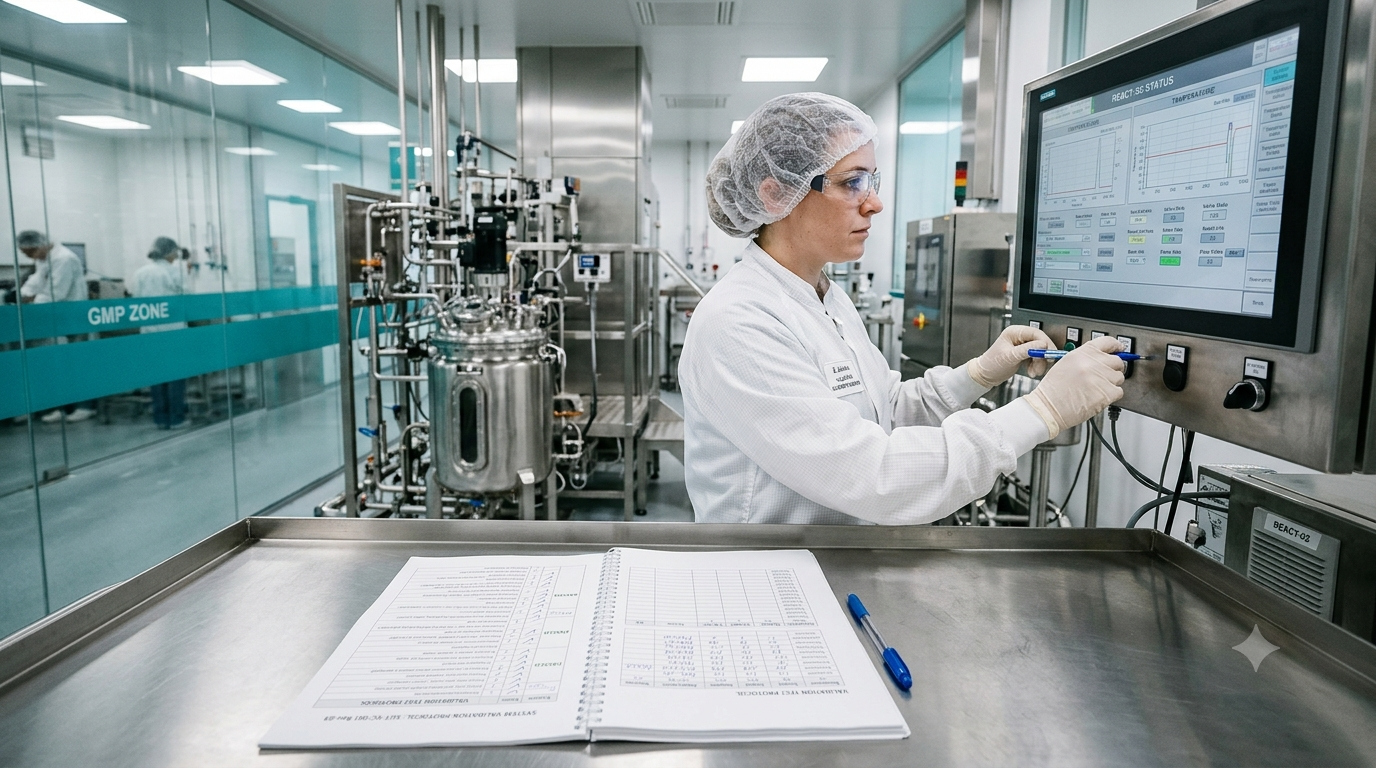
Computer System Validation Process in a GMP pharmaceutical facility, showing an engineer reviewing validation documents beside a computerized manufacturing system.
✓

QUICK ANSWER

Computer System Validation (CSV)

What Is the Computer System Validation Process?

The computer system validation process is a documented, risk-based approach to demonstrating that a computerized system performs as intended and meets applicable GMP and business requirements.

|  KEY STAGES

Planning → Requirements → Risk Assessment → Testing → Reporting → Ongoing Control

✓

Key Takeaways

The essential points to understand about computer system validation.

✓

Risk-based approach

Validation effort should reflect the system’s intended use, GxP impact, and risk.

✓

Documented evidence

Requirements, risk assessments, test results, and approvals provide evidence that the system works as intended.

✓

Lifecycle control

Changes, access, incidents, and periodic reviews help maintain the validated state.

Laboratory systems, batch record platforms, and PLCs can each affect product quality or data integrity, so regulators expect evidence that they work as intended. The computer system validation process provides that evidence. This guide explains seven practical steps, key documents, and how to keep systems validated.

Why GMP Computer System Validation Matters

Computerized systems create, process, and store GxP records. If a system calculates incorrectly or allows untraceable changes, release decisions rest on unreliable data.

Regulations Versus Guidance

Requirements differ by region and by system. In the US, 21 CFR Part 11 applies to electronic records and signatures that fall within its scope, and FDA’s scope and application guidance explains how the agency approaches it. For drug manufacturing, 21 CFR Part 211 includes §211.68 on automatic, mechanical, and electronic equipment, but its provisions do not apply identically to every system.

In the EU, EU GMP Annex 11 is relevant to computerised systems used in GMP-regulated activities, and Annex 15 covers qualification and validation (see EudraLex Volume 4). The European Commission released a draft revision of Annex 11 for public consultation in 2025. The consultation closed on 7 October 2025; the current published Annex 11 remains listed as the January 2011 revision. GAMP 5 from ISPE is industry guidance that supports a risk-based approach but does not replace applicable regulations.

CSV and CSA are related but are not interchangeable regulatory terms. FDA’s Computer Software Assurance (CSA) guidance addresses software used in medical-device production and quality management systems. It should not be treated as a universal replacement for pharmaceutical CSV requirements.

The 7 Key Steps in the Computer System Validation Process

Treat these steps as a practical, risk-based lifecycle model. They are not a legally mandated sequence, and companies adapt them to their quality systems.

Step 1: Define Intended Use and Scope

Start with what the system does and which processes, records, and users it touches. A stability chamber monitoring system and an ERP module used for batch release have very different scopes. For PLC-controlled equipment, coordinate computer system validation (CSV) with equipment qualification to ensure that both the equipment and its computerized control functions are assessed for their intended use. Learn more about pharmaceutical equipment qualification.

Step 2: Assess GxP Impact and Risk

Decide whether the system affects patient safety, product quality, or data integrity, then assess its risks. In a computer system validation risk assessment, a batch record calculation may rate high, while a report’s cosmetic layout rates low. Those ratings guide testing depth.

Step 3: Establish Requirements and Plan Validation

Write user requirements that are clear, testable, and tied to intended use. For a laboratory system, examples include unique logins and audit trails for result changes. Then prepare a validation plan covering roles, deliverables, test approach, and acceptance criteria.

Step 4: Review Supplier Documentation and Specifications

Assess the supplier’s quality system and, where justified, use their testing evidence rather than repeating it. Prepare functional or design specifications for configured or custom elements. Standard functions may need less testing when the risk assessment and available supplier evidence justify it.

Step 5: Execute Risk-Based Testing and Record Evidence

Match testing to risk. Functions with high impact, such as electronic signatures or calculations, often justify scripted tests with predefined expected results. Lower-risk functions may be covered by lighter methods. Intended use, applicable requirements, and approved procedures should justify the depth you choose. Record actual results, who tested, and when, so an independent reviewer can reach the same conclusion.

Step 6: Manage Deviations and Maintain Traceability

Tests sometimes fail. Record each deviation, assess its impact, correct the cause, and retest. A requirements traceability matrix shows whether every requirement has test coverage and links failures to their deviation records.

Step 7: Prepare the Summary Report and Approve Release

Summarize the work, test results, deviations, and conclusion on whether the system is fit for its intended use. Obtain the required approvals under the company’s quality system before releasing the system for GxP use. Confirm that required documentation is approved, deviations are closed or formally justified, users are trained, procedures are effective, and access and backup controls are in place.

Computer System Validation Documentation

The documents required depend on system complexity, risk, intended use, supplier evidence, and the applicable quality system. Not every system needs the same set.

Core Deliverables

Key documents and evidence required during the CSV process

✓

Validation plan

Defines the scope, approach, and responsibilities.

✓

User Requirements Specification (URS)

Documents what the system must do.

✓

Risk assessment

Identifies risks and determines where validation effort should focus.

✓

Functional or design specifications

Describe system functions or design details, where applicable.

✓

Requirements Traceability Matrix

Connects requirements with specifications, tests, and results.

✓

Test protocols and executed evidence

Records test procedures, actual results, and supporting evidence.

✓

Deviation records

Document issues identified during testing and how they were resolved.

✓

Validation summary report

Summarises the validation outcome and provides the basis for release.

Computer System Validation Traceability Matrix

Example of a CSV Traceability Matrix

A traceability matrix links each system requirement to its corresponding test and recorded result. The example below illustrates how requirements can be tracked during computer system validation.

Requirement ID Requirement Test ID Result Deviation Reference
URS-001 Only authorised users can access the system TC-001 Pass None
URS-002 Relevant user activities are recorded in the audit trail TC-002 Pass None
URS-003 User access permissions can be assigned by role TC-003 Fail DEV-001

Note: This is an illustrative example, not an actual validation record. Failed tests should be documented, investigated and handled according to approved procedures.

Maintaining the Validated State

Validation does not end at go-live. Change control, periodic review, access management, backup and restore checks, and incident handling keep the system in a validated state. These controls also protect data integrity. Significant changes, such as software upgrades, new interfaces, or configuration changes affecting GxP records, may call for impact assessment and targeted retesting. The review frequency should follow risk and your procedures, not a fixed calendar rule.

How IncepBio Supports Computer System Validation

IncepBio supports pharmaceutical companies with risk-based Computer System Validation (CSV) and Computer Software Assurance (CSA) throughout a system’s lifecycle, from planning to regular reviews.

  • Planning and Risk Assessment: Defines system requirements, reviews risks, and prepares validation plans.
  • Testing and Documentation: Supports IQ, OQ, and PQ testing, requirement tracking, and validation reports.
  • Compliance Checks: Reviews systems against 21 CFR Part 11 and EU GMP Annex 11 and identifies gaps that need attention.
  • Data Integrity: Reviews audit trails, user access, and electronic signatures to help protect data.
  • Supplier Assessment: Reviews supplier quality and available documents to plan suitable validation activities.
  • Ongoing Support: Supports change control, periodic reviews, revalidation, and system retirement.

Systems Covered

IncepBio supports validation for laboratory systems (LIMS and CDS), manufacturing systems (PLC, SCADA, HMI, DCS, and MES), enterprise systems (ERP), quality management systems (eQMS), and facility monitoring systems (BMS and EMS).

Explore IncepBio’s CSV/CSA services to learn more.

Conclusion

A reliable computer system validation process starts with clear intended use, documented requirements and a risk-based approach to testing. Pharmaceutical companies should also maintain traceable evidence, manage deviations and assess system changes throughout its lifecycle.The validation approach and documentation should reflect the system's intended use, complexity and impact on product quality, patient safety and data integrity. With appropriate planning and ongoing controls, organisations can maintain systems in a validated state and support GMP compliance.

Frequently Asked Questions

What is the computer system validation process in pharma?

It is a documented, risk-based process showing that a GxP computerized system performs as intended. It links intended use, requirements, testing, and approval, and then continues through change control and periodic review.

Common steps are defining intended use, assessing risk, setting requirements and a plan, reviewing supplier evidence, testing, managing deviations and traceability, and approving a summary report. Companies adapt this sequence to their procedures.

Typical documents include a validation plan, URS, risk assessment, test evidence, traceability matrix, deviation records, and a summary report. The exact set depends on system complexity, risk, supplier evidence, and the company’s quality system.

GAMP 5 is an ISPE industry guidance that scales validation effort to system category, complexity, and risk. It helps teams apply critical thinking, but it does not replace regulatory requirements such as Part 11 or Annex 11.

There is no universal fixed interval. Review or revalidation depends on changes, risk, system performance, and your procedures. Periodic reviews check the validated state, and significant changes may trigger targeted retesting.

NEED EXPERT SUPPORT?

Looking for CSV/CSA Support for Your Pharma Systems?

Contact IncepBio to discuss your computer system validation requirements and the support your project may need.

Explore CSV/CSA Services →